CI/CD & Source Control (GitLab)

Project information
- Category: DevOps
- Client: INSTAR Deutschland GmbH (Waletech) Shenzhen, China
- Project date: 01 March, 2018
- Project URL: gitlab.com
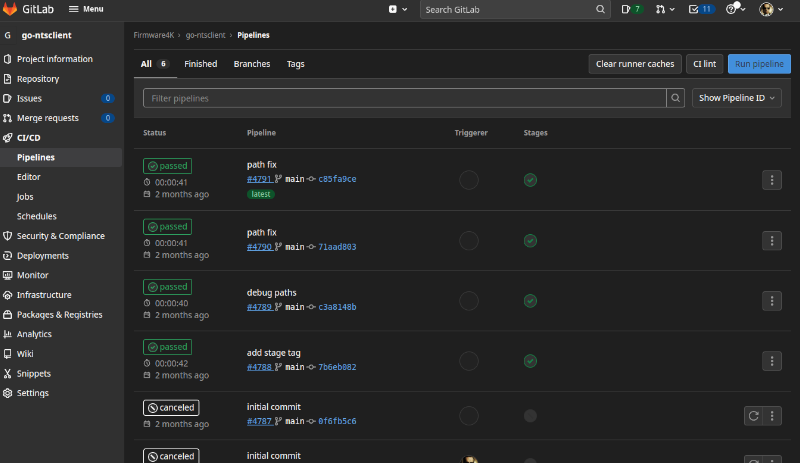
The problem: production reached by manual SSH, patch by patch — inconsistent, untracked, and impossible to roll back cleanly. What I did: Everything — product code, infrastructure-as-code (Nomad job files), and ML model artifacts — lives in a self-hosted GitLab EE server, which I also deploy and operate as a Nomad job with the container registry, Let's Encrypt auto-renewal, and a hardened three-tier backup/restore procedure (DB+repos, then registry, then artifacts) so the whole platform is recoverable in minutes, not hours. The pipeline wraps source in Docker, runs tests, and pushes the artifact to the internal registry; the Nomad driver pulls it on merge with canary rollout and automatic rollback on a failing health check. Protected environments plus a per-namespace ACL policy mean a merge can't ship to a namespace the author isn't allowed to touch. It is now the single path through which every web service, AI model, and infra change reaches production. The payoff: the difference between "deploys" and "shipping at fleet scale."